What Is a Jump Box and How Does It Work?
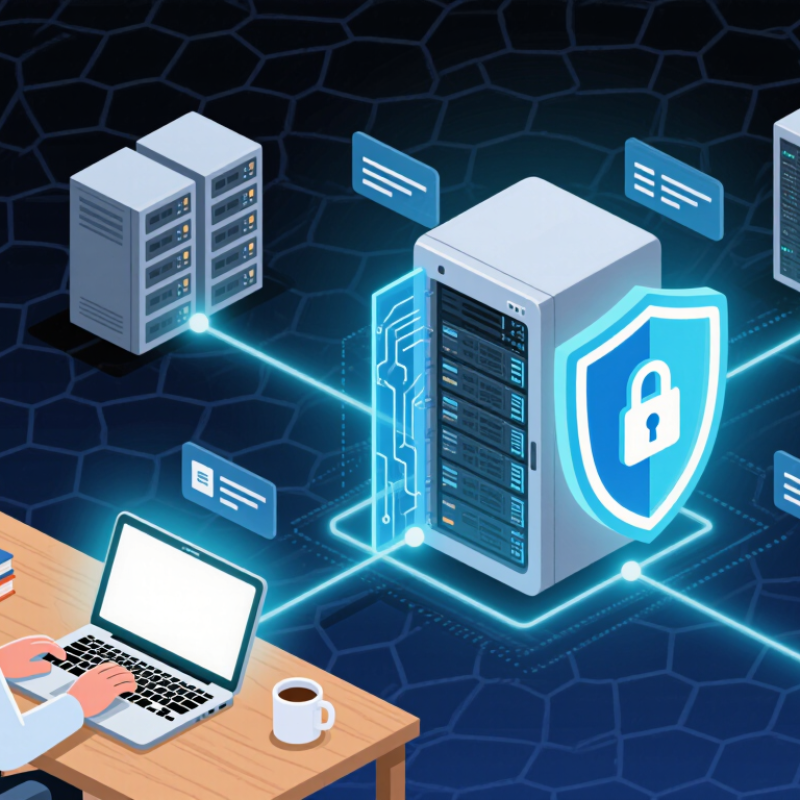
A Jump Box, also called a bastion host or jump server, creates a controlled doorway into a protected network. Instead of connecting directly to a database, industrial system, or private server, an administrator first signs into the Jump Box. The box then provides a second, monitored connection to the internal resource.
Picture an engineer working from a laptop at home. They connect through an approved VPN, complete multi-factor authentication, and reach a hardened Jump Box. From there, they access only the systems assigned to their role. Security teams can record login times, commands, device details, and session duration. This narrow route reduces exposure and makes unusual activity easier to investigate.
Bruce Schneier’s well-known warning applies here: “Security is a process, not a product.” A Jump Box supports that process, but it does not replace careful security management. It needs timely patches, strong access controls, restricted tools, and continuous log review. File transfers and clipboard sharing should also receive close attention. Small conveniences can create large weaknesses.
The design is not magic. A poorly configured Jump Box may become the most attractive target in the environment. It can also create false confidence when administrators overlook stolen credentials or outdated software. That uncomfortable possibility matters. This guide will examine what a Jump Box does, how traffic moves through it, and where its practical limits appear. The goal is a clear, realistic view, not a promise of perfect protection.
What Is a Jump Box and What Role Does It Serve?
A jump box, or bastion host, is a controlled gateway between an administrator and sensitive systems. Its main role is to reduce direct access to private servers. Instead of connecting from a laptop to a database, an administrator first enters the jump box. The box then passes approved connections to the target system.
This design creates a visible checkpoint. Security teams can enforce multi-factor authentication, restrict source addresses, record sessions, and remove unnecessary tools. A 2024 Data Breach Investigations Report found that the human element appeared in 68% of breaches. Centralized administrative access can reduce careless exposure, although it cannot correct weak passwords or poor approval practices. A 2024 global data-breach cost report placed the average breach cost at 4.88 million dollars. One gateway is not a complete defense.
Tips: Keep the jump box minimal. Install only required management tools. Place it in a separate network segment, patch it quickly, and use short-lived accounts. Log commands, not just login times. Test whether alerts work during a real maintenance window. This is often overlooked. Access rules should also expire automatically, because old permissions quietly become permanent. A jump box can become a dangerous single target if administrators store credentials on it or allow unrestricted internal movement. Review its logs weekly, and question every account that still needs access.
How a Jump Box Controls Access to Protected Systems
A jump box is a hardened intermediary server between administrators and protected systems. Instead of connecting directly to a database or production host, a user first enters the jump box through a controlled gateway. The box verifies identity, applies access rules, and forwards approved sessions. It can also record commands, source addresses, and connection times. The arrangement creates a narrow doorway. Not a magic wall.
Access control becomes stronger when the jump box follows least-privilege principles. A database engineer may reach one database port, while a systems operator receives temporary shell access. Multi-factor authentication, device checks, short session limits, and separate administrator accounts reduce exposure. The 2024 Data Breach Investigations Report found that the human element appeared in 68% of breaches. A jump box cannot remove mistakes, but it can make risky actions visible and easier to stop.
Operational discipline matters more than installing the server. Administrators should patch the jump box, disable unused tools, restrict outbound traffic, and send logs to independent monitoring. The 2024 Cost of a Data Breach Report placed the global average breach cost at 4.88 million dollars, showing why privileged access deserves careful control. Still, centralized access can create a dangerous single point of failure. If credentials, logging, or the box itself are poorly protected, the gateway may become the attacker’s preferred target. This is where many teams need more reflection. Controls must be tested during real maintenance, not only documented during audits.
What Is a Jump Box and How Does It Work?
Common management protocol ports controlled at a jump box
A jump box is a hardened intermediary system used to reach protected servers. Administrators connect to the jump box first, where identity verification, authorization rules, logging, and network policies can be applied before management traffic is allowed to continue. The chart shows standard port numbers associated with commonly used management protocols; a jump box can restrict which users may access each protocol and destination.
Typical Jump Box Connection Workflow
What Is a Jump Box and How Does It Work?
A jump box is a controlled access server between an operator and protected systems. It creates one monitored entry point. In a typical workflow, the operator connects to the jump box through an encrypted channel. Identity checks happen before any internal connection is allowed. Multifactor authentication adds another barrier.
The jump box then checks the requested destination, account, and permission level. If approved, it opens a second connection to the target server. The operator may use a secure shell session, a remote desktop session, or another approved management protocol. Network rules usually block direct access from the user’s device. This reduces exposure and simplifies auditing. Session records can include login time, destination, commands, and logout status.
Keep it narrow.
A well-managed setup uses separate accounts, short-lived credentials, and carefully limited access rights. Administrators should patch the jump box regularly and remove unused tools. They should also test emergency access before an outage occurs. A common mistake is treating the jump box as a trusted shortcut. It is still a high-value system. In practice, rushed permission changes can create hidden paths around the intended workflow. Reviewing access logs by hand may feel slow, but automated alerts can miss context. Clear procedures, tested backups, and periodic access reviews make the connection process more dependable.
Security Benefits, Limitations, and Best Practices
A jump box is a hardened computer used as a controlled gateway to private systems. Administrators connect to it before reaching servers, databases, or network devices. This design reduces direct exposure and creates a clearer access path. In practice, a well-configured jump box can centralize authentication, session logging, and administrative tools. That visibility supports investigations when an unusual login appears.
Its security value depends on strict controls. Use separate administrator accounts, multi-factor authentication, and short-lived access permissions. Permit connections only from approved networks or managed devices. Remove unnecessary software and block ordinary web browsing. Apply security updates quickly, then verify that essential services still work. Small mistakes matter. A forgotten firewall rule can weaken the entire boundary.
A jump box is not a complete security solution. If attackers compromise it, connected environments may become easier to reach. Excessive privileges create the same danger. Limit reachable systems, restrict command tools, and monitor login times, source addresses, and session activity. Store logs separately with protected retention. Test recovery procedures, too. Teams sometimes record sessions but never review them. That weakens their value. Periodic access reviews should remove inactive accounts and confirm every permission still has a business reason. More isolation is not always better if emergency access becomes confusing or untested.